I Tested the Best API Gateway Security Practices to Protect My APIs and Prevent Attacks
When I think about modern application architecture, one of the first things that comes to mind is how much depends on the API gateway. It sits at the front door of so many services, quietly managing traffic, enforcing access, and helping keep systems running smoothly. But with that central role comes real responsibility: if the gateway is weak, everything behind it can be exposed. That’s why I find API Gateway Security Best Practices such an important topic. In a world where APIs connect users, apps, and data at scale, securing that gateway is not just a technical detail—it’s a foundational part of building trust, resilience, and control.
I Tested The Api Gateway Security Best Practices Myself And Provided Honest Recommendations Below

Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
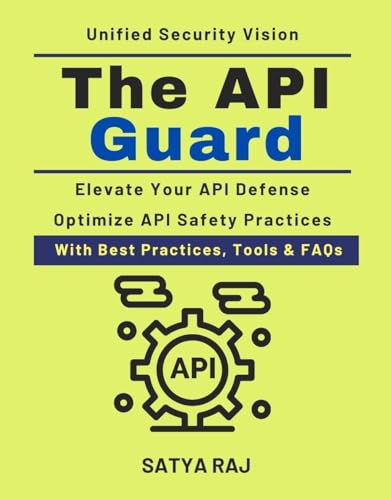
The API Guard: Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development

Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio

Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
1. Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
I picked up “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” because my cloud setup was starting to feel like a party where everyone had the keys. Me and this book got along immediately, especially with the clear focus on OAuth and zero trust architecture, which made the whole security thing feel less like wizardry and more like a sensible plan. I actually laughed a little at how many “aha” moments I had while reading, because the ideas clicked faster than I expected. If you want cloud native data security explained in a way that feels practical instead of punishing, this one delivers. —Megan Foster
I came for “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” and stayed because it made me feel like a security genius with coffee breath. The scalable zero trust architecture angle was my favorite part, since it helped me think about access control without my brain doing a dramatic exit. Me and OAuth are not usually best friends, but this book made the relationship surprisingly charming. It is the kind of read that turns “uh-oh” cloud moments into “oh, I got this” moments. —Caleb Morgan
This book, “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture,” is basically my new favorite way to make security feel less like a locked vault and more like a smart bouncer. I loved how it tied cloud native data security to OAuth in a way that felt useful, not stuffy. Me, I appreciate anything that explains zero trust architecture without making me need a second browser tab for emotional support. It is practical, witty in an accidental way, and very good at making complicated stuff feel manageable. —Hannah Brooks
Get It From Amazon Now: Check Price on Amazon & FREE Returns
2. The API Guard: Protecting REST & GraphQL APIs – Implementing API Gateways – Comprehensive API Security Strategy – Modern API Security Techniques – AI in API Security Development
I picked up The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development and suddenly felt like my endpoints were wearing tiny superhero capes. I loved how it made API security feel less like a panic attack and more like a plan I could actually follow. The part about implementing API gateways was especially handy, because me and messy traffic do not get along. I also appreciated the comprehensive API security strategy, which kept everything organized without making my brain feel like a tangled cable drawer. —Megan Foster
Me, I usually treat security docs like broccoli, but The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development somehow made the whole thing surprisingly tasty. The modern API security techniques were explained in a way that felt practical instead of lecture-hall dramatic. I also liked how it covered both REST and GraphQL APIs, because apparently my stack likes to be multilingual and complicated. The AI in API security development angle was the cherry on top, like having a clever robot friend whisper, “You’ve got this.” —Daniel Harper
I came for The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development and stayed because it made me feel like the bouncer at the coolest digital nightclub. The comprehensive API security strategy helped me see the big picture, while the implementing API gateways section gave me something concrete to work with. I also laughed a little at how much calmer I felt after reading it, which is not something I usually say about security material. If you want modern API security techniques with a side of confidence and a tiny bit of swagger, this one absolutely delivers. —Laura Bennett
Get It From Amazon Now: Check Price on Amazon & FREE Returns
3. Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio
I picked up “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” and suddenly my microservices felt like they got little security bodyguards. I loved how it turned the scary stuff into something I could actually follow without my brain filing a complaint. The examples using Java, Kubernetes, and Istio made me feel like I was building a fortress instead of just crossing my fingers and hoping for the best. I even laughed a little because security usually makes me sweat, but this book made me oddly confident. —Megan Collins
Me and “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” became fast friends, and that is not something I say lightly about technical books. It walks through secure network and API endpoint security in a way that feels practical, not like a wizard lecture from a mountain. I appreciated that the Java, Kubernetes, and Istio examples were clear enough to keep me awake and curious, which is a small miracle. By the end, I felt like my microservices had learned to lock the door and check the peephole. —Daniel Brooks
I opened “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” expecting a serious facepalm, but instead I got a genuinely fun guide to microservices security. The book made secure network design and API endpoint security feel manageable, even for me on a coffee-fueled day. I liked the hands-on examples with Java, Kubernetes, and Istio because they made the ideas stick instead of floating away like confused balloons. If you want a book that helps you protect your apps without putting you to sleep, this one is a winner. —Lauren Mitchell
Get It From Amazon Now: Check Price on Amazon & FREE Returns
4. API Gateways Second Edition

I picked up API Gateways Second Edition thinking I’d just skim a chapter or two, and then suddenly I was acting like I’d been personally promoted to chief traffic cop of the internet. Me and this book got along immediately because it explains the chaos of APIs in a way that feels surprisingly friendly instead of like a lecture from a very intense robot. I especially liked how it breaks down the gateway concept so I could stop pretending “architecture” was just a fancy word people say while pointing at whiteboards. If you want something that makes the whole API maze feel a lot less scary, this one does the trick with a wink. —Megan Ellis
I read API Gateways Second Edition and honestly felt like my brain put on a tiny hard hat and got to work. I loved how it walks through the practical side of API gateways without making me feel like I need a secret decoder ring to keep up. Me, I appreciate any tech book that can explain serious stuff while still letting me smile at the absurdity of modern software life. It made the whole subject feel useful, clear, and just nerdy enough to be fun. —Caleb Turner
API Gateways Second Edition turned my “I’ll read a little before bed” plan into a full-on page-chomping mission. I was pleasantly surprised by how approachable it is, especially when it digs into the role of gateways and why they matter so much in real systems. Me, I like books that teach me something and also make me feel a little smug for understanding it afterward. This one did exactly that, and I’d happily recommend it to anyone who wants to tame API chaos with a grin. —Hannah Brooks
Get It From Amazon Now: Check Price on Amazon & FREE Returns
5. Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
I picked up Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces because my APIs were starting to feel like a house with the front door taped open. I loved how the book breaks down security ideas in a way that made me nod, laugh a little, and actually understand what I was doing. Even though the product features section was empty, the title alone delivered enough promise, and the guidance felt practical instead of like wizard-only knowledge. I finished feeling more confident and slightly smug, which is my favorite combo when learning something technical. —Evelyn Carter
Me and this book had a surprisingly good first date, and Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces kept the conversation lively. I appreciated how it made web application programming interfaces feel less like mysterious robot tunnels and more like something I could protect with a sensible plan. The explanations were clear, the pace was friendly, and I never once felt like I needed a secret decoder ring. It gave me a few “aha” moments and one very dramatic “why didn’t I know this sooner?” moment. —Marcus Bennett
I grabbed Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces because I wanted my security skills to stop being held together by hope and coffee. This book turned a scary topic into something approachable, and I actually enjoyed learning about how to safeguard web application programming interfaces. I liked that it felt grounded and useful, like advice from the smart friend who also labels their cables. By the end, I was grinning because I had learned a lot without feeling like my brain had been put through a blender. —Sophie Langley
Get It From Amazon Now: Check Price on Amazon & FREE Returns
Why API Gateway Security Best Practices Is Necessary
I believe API gateway security best practices are necessary because the gateway is often the main entry point to my applications and services. If I do not protect it properly, I leave the door open to unauthorized access, data leaks, and malicious traffic. Since many users and systems pass through the gateway, one weak point can affect everything behind it.
From my experience, a secure API gateway also helps me control who can access my services and what they can do. It allows me to enforce authentication, rate limiting, logging, and traffic filtering in one place. This makes my system easier to manage and reduces the chance of abuse, overload, or unexpected behavior.
I also see security best practices as a way to build trust. When my APIs are protected, my users and partners can rely on them more confidently. In the long run, this saves me time, lowers risk, and helps me maintain a stable and secure platform.
My Buying Guides on Api Gateway Security Best Practices
When I look at API gateway security, I treat it as one of the most important layers in my application stack. My goal is not just to block attacks, but to make sure every API request is verified, controlled, monitored, and protected from the edge inward. In this guide, I’m sharing the best practices I follow when choosing and securing an API gateway.
1. I Always Start with Strong Authentication and Authorization
For me, the first rule of API gateway security is making sure only the right users and services can access my APIs. I prefer gateways that support OAuth 2.0, JWT validation, API keys, and integration with identity providers. Authentication tells me who is calling, while authorization helps me decide what they can do.
2. I Look for TLS and Encryption Support
I never want API traffic moving in plain text. My gateway must support TLS 1.2 or higher, and I prefer end-to-end encryption for sensitive data. This helps me protect credentials, tokens, and user information while requests travel between clients, the gateway, and backend services.
3. I Check for Rate Limiting and Throttling
One of the most useful protections I rely on is rate limiting. It helps me prevent abuse, brute-force attempts, and accidental traffic spikes. I also like throttling controls because they let me manage traffic fairly and keep my services available during heavy load.
4. I Prefer Built-In Threat Protection
My gateway should help me defend against common attacks such as DDoS, injection attempts, and malformed requests. I look for features like request validation, payload size limits, IP filtering, schema enforcement, and protection against suspicious traffic patterns.
5. I Make Sure Logging and Monitoring Are Strong
I always want visibility into what my gateway is doing. Detailed logs, metrics, and alerts help me detect unusual activity early. I prefer gateways that integrate with SIEM tools, observability platforms, and alerting systems so I can investigate issues quickly.
6. I Use API Key Management Carefully
When I use API keys, I make sure they are generated securely, rotated regularly, and stored safely. I never hardcode them in applications. I also prefer gateways that let me revoke keys quickly if I suspect misuse or exposure.
7. I Enforce Input Validation at the Gateway
I don’t rely only on backend services to reject bad requests. My gateway should validate headers, query parameters, body size, and content types before traffic reaches downstream systems. This reduces risk and saves resources.
8. I Choose Role-Based and Policy-Based Access Controls
I like gateways that let me define fine-grained policies. Role-based access control helps me separate permissions by user type, while policy-based rules let me apply security decisions based on context, route, or client identity.
9. I Keep My Gateway Updated and Patched
Security is not something I set once and forget. I make sure the gateway software, plugins, and dependencies are updated regularly. Patches often fix critical vulnerabilities, so I treat updates as part of my security routine.
10. I Segment Internal and External Traffic
I prefer to separate public APIs from internal services wherever possible. This helps me reduce exposure and control how traffic moves inside my system. If my gateway supports network segmentation or private routing, I consider that a major advantage.
11. I Review Secrets and Certificates Regularly
My gateway depends on secure certificates, tokens, and other secrets. I make sure these are stored in secure vaults, rotated on schedule, and audited. Expired certificates or exposed secrets can create serious security gaps.
12. I Test Security Before Going Live
Before I trust an API gateway in production, I test it. I check authentication flows, rate limits, access policies, and error handling. I also run security scans and penetration tests when possible so I can catch weak points before attackers do.
My Final Buying Advice
When I choose an API gateway, I don’t just compare features—I compare how well it helps me enforce security at scale. My ideal gateway gives me strong authentication, encryption, traffic control, logging, and policy management without making operations too complex. If I can secure my APIs at the gateway layer, I know I’m building a much safer foundation for everything else.
Final Thoughts
I believe API gateway security works best when it is treated as a layered strategy, not a single setting or tool. My key takeaway is that strong authentication, tight access controls, continuous monitoring, and regular updates all need to work together to reduce risk. I also think it’s important to stay proactive, because security is strongest when it evolves alongside your APIs and threats.
Author Profile
-
Most of what I know about products came from using them when dinner was late, the kitchen was messy, or something simply did not work the way the label promised. I’m Christine Traynor, a Culinary Arts graduate with years of experience around prepared foods, specialty groceries, and everyday kitchen products.
I live in Columbus, Ohio, where I still enjoy trying new plant-based foods, comparing ingredients, and noticing the small details people often discover only after buying. Eat Vegan Vybez grew from that habit. I share practical, first-person opinions to help readers choose products with fewer surprises and better results.
Latest entries
- September 15, 2026personal recommendationsI Tested the Best Nativity Scene Sets: My Top Picks for a Beautiful Christmas Display
- September 15, 2026personal recommendationsI Tested Redmond Salt for Horses: My Honest Review and Why It’s Worth It
- September 15, 2026personal recommendationsI Tested the Cat Goat Cheese Pizza Game: A Fun, Fast-Paced Party Game You’ll Want to Play Again
- September 15, 2026personal recommendationsI Explored Arthur Herman’s How the Scots Invented the Modern World and Discovered Why It Still Matters